Hardware security · Self-hosted AI · Founded 2025

Own your root of trust. Keep your AI in‑boundary.

RAE is a hardware-security startup building BootProtect — post-quantum, owner-controlled secure boot that retrofits FPGAs already in the field — and Reg, the self-hosted AI engineering companion that keeps CUI and ITAR work inside your security boundary.

Securing today's systems from tomorrow's threats

Our technology

Four products. One thesis: you should own your security.

Silicon IP that makes fielded FPGAs quantum-safe and keeps host boot firmware encrypted at rest and on the wire — and a self-hosted AI platform that brings frontier-class engineering assistance inside the compliance boundary.

BootProtect

Patent-pending Errantry IP · with IC-Safety

Today's roots of trust are manufacturer-anchored: a vendor-fused key, checked by RSA/ECC hard logic that can't be patched. CNSA 2.0 puts National Security Systems on a 2030–2035 post-quantum timeline — and for fielded FPGAs, the only conventional path is replacing the silicon.

BootProtect re-creates the bitstream decryption key from the chip's own silicon fingerprint — nothing stored, nothing to extract, no asymmetric cryptography anywhere in the chain.

  • Retrofit, not replace: reconfiguration alone, no recertification
  • Post-quantum by construction: AES-256 + SHA2, zero asymmetric primitives
  • Owner-controlled keys with in-field re-keying
  • SiRF PUF independently assessed by Sandia National Laboratories
BootProtect — post-quantum, owner-controlled secure boot for fielded FPGAs PATENT-PENDING ERRANTRY IP · WITH IC-SAFETY TODAY — MANUFACTURER-ANCHORED SECURE BOOT Vendor-fused key eFuse · mask ROM · helper data RSA / ECC signature check hard logic — not patchable Boot ✗ the manufacturer owns your trust anchor ✗ classical crypto falls to quantum — and is fixed in silicon ✗ CNSA 2.0 fix = replace the silicon WITH BOOTPROTECT Power-on SiRF PUF unique silicon fingerprint recreates Boot key from PoRB never stored — owner-enrolled Authenticate + decrypt design AES-256 + SHA2 — no asymmetric Boot ✓ retrofits FPGAs already in the field ✓ nothing stored to steal ✓ post-quantum by construction • TAMPER-EVIDENT — any change to the protected bitstream breaks key re-creation and blocks boot • DPR TEARDOWN — BootProtect vacates the fabric after handoff; steady-state footprint approaches zero • CNSA 2.0 — meets the post-quantum transition through reconfiguration alone, years ahead of a silicon refresh

Manufacturer-anchored boot vs. BootProtect's owner-controlled, symmetric-only chain.

AES Crypto

Patent pending

Even strong cryptography leaks. Power-analysis attacks (SPA/DPA) recover secret keys by watching a chip's power draw. AES Crypto — the side-channel-hardened engine inside BootProtect, also available as standalone IP — makes those attacks see only noise.

  • Dual AES cores in lock-step, exchanging valid and decoy data
  • PUF-based TRNG injects fresh masking into every operation
  • Same block, different power signature — every single run
  • Drops in as a VHDL block on most FPGA families
Talk to us about licensing →
AES Crypto — side-channel-hardened AES with integrated PUF PATENT PENDING PUF-based TRNG fresh random masks, every operation mask mask Data block plaintext in AES core A lock-step instance 1 AES core B lock-step instance 2 valid ⇄ decoy data exchange Data block ciphertext out power draw WHAT AN ATTACKER MEASURES — SAME BLOCK, TWO RUNS run 1 run 2 The power signature differs on every operation — even for the identical block — so SPA/DPA analysis sees only noise.

Masked lock-step execution: an attacker never sees the same power signature twice.

Mithril

HAIR-compliant boot-flash root of trust

A platform's earliest boot code lives in SPI flash outside the host's security perimeter — readable, copyable, and alterable with inexpensive bus-level tools before any software defense has begun to run. Native boot protections are fixed in host silicon and leave the image bare on the medium and on the wire.

Mithril sits transparently inline on the SPI path. The boot image stays encrypted at rest; Mithril decrypts it on-the-fly and re-encrypts everything returned to the host under keys bound to a live platform attestation — derived at run time, never stored. No change to the host, the flash device, or the boot software. To our knowledge, it is the only HAIR-compliant hardware root of trust in existence.

  • Transparent inline insertion — the host sees a standard SPI flash
  • Attestation-bound AES-256-GCM, at rest and in transit; no static secret to recover
  • Proven on hardware: an Intel Ice Lake-D host boots through Mithril inline
  • Vendor-portable FPGA logic — Microchip and Lattice today, AMD/Xilinx and Altera underway
  • Post-quantum upgrade path through BootProtect
Read the Mithril brief →
Validated on
Intel Ice Lake-D · Microchip PolarFire MPF300T
Cryptography
AES-256-GCM (NIST SP 800-38D) — no asymmetric primitives on the data path
Attestation
SPDM 1.3 mutual attestation gates every session
Key management
Session keys derived at run time, never stored · in-field re-keying
Licensing
One-time perpetual license · full source-code access

The host completes bootstrap discovery and loads its full boot image through Mithril — captured end to end on RAE's bit-accurate SPI instrument.

Reg

Self-hosted · CUI/ITAR-safe · U.S.-origin models

Commercial AI assistants process every prompt in a vendor cloud — disqualifying for CUI and ITAR work. Reg inverts the trust model: the data stays put, and the models come to it.

Air-gapped on hardware you own, Reg is a full engineering copilot — chat, documents, mail and calendar with human-approval gates — plus a verified FPGA/VHDL toolchain no other AI system offers.

  • No prompt, document, or design ever leaves your boundary
  • U.S.-origin models only — no PRC-origin weights, even air-gapped
  • Verified VHDL: only code that passes simulation ships
  • FPGA sign-off across Microchip, Lattice, AMD/Xilinx, Altera
  • In production today — Reg runs RAE's own engineering
Read the Reg brief →
Reg — the in-boundary AI companion for the Defense Industrial Base SELF-HOSTED · U.S.-ORIGIN MODELS YOUR SECURITY BOUNDARY — AIR-GAPPED, CUSTOMER-OWNED HARDWARE Your team AD login, per-user Reg chat · documents · mail + calendar draft → approve gates outbound REASONING LADDER Fast local router — 30B everyday chat + tool use Deep reasoning — 120B hard multi-step problems Frontier — 400B-class hardest reasoning + long context escalates VERIFIED FPGA / VHDL TOOLCHAIN generate → compile → simulate → repair — only code that passes ships implementation sign-off on 4 vendors: Microchip · Lattice · AMD/Xilinx · Altera synthesis → place & route → timing → bitstream, hundreds of modules verified per vendor Cloud AI vendor-hosted assistants ✗ ROUTING GUARD: non-CUI work only — controlled data never leaves the boundary • U.S.-ORIGIN MODELS ONLY — no PRC-origin weights, even air-gapped • IN PRODUCTION TODAY — Reg runs RAE's own daily engineering work
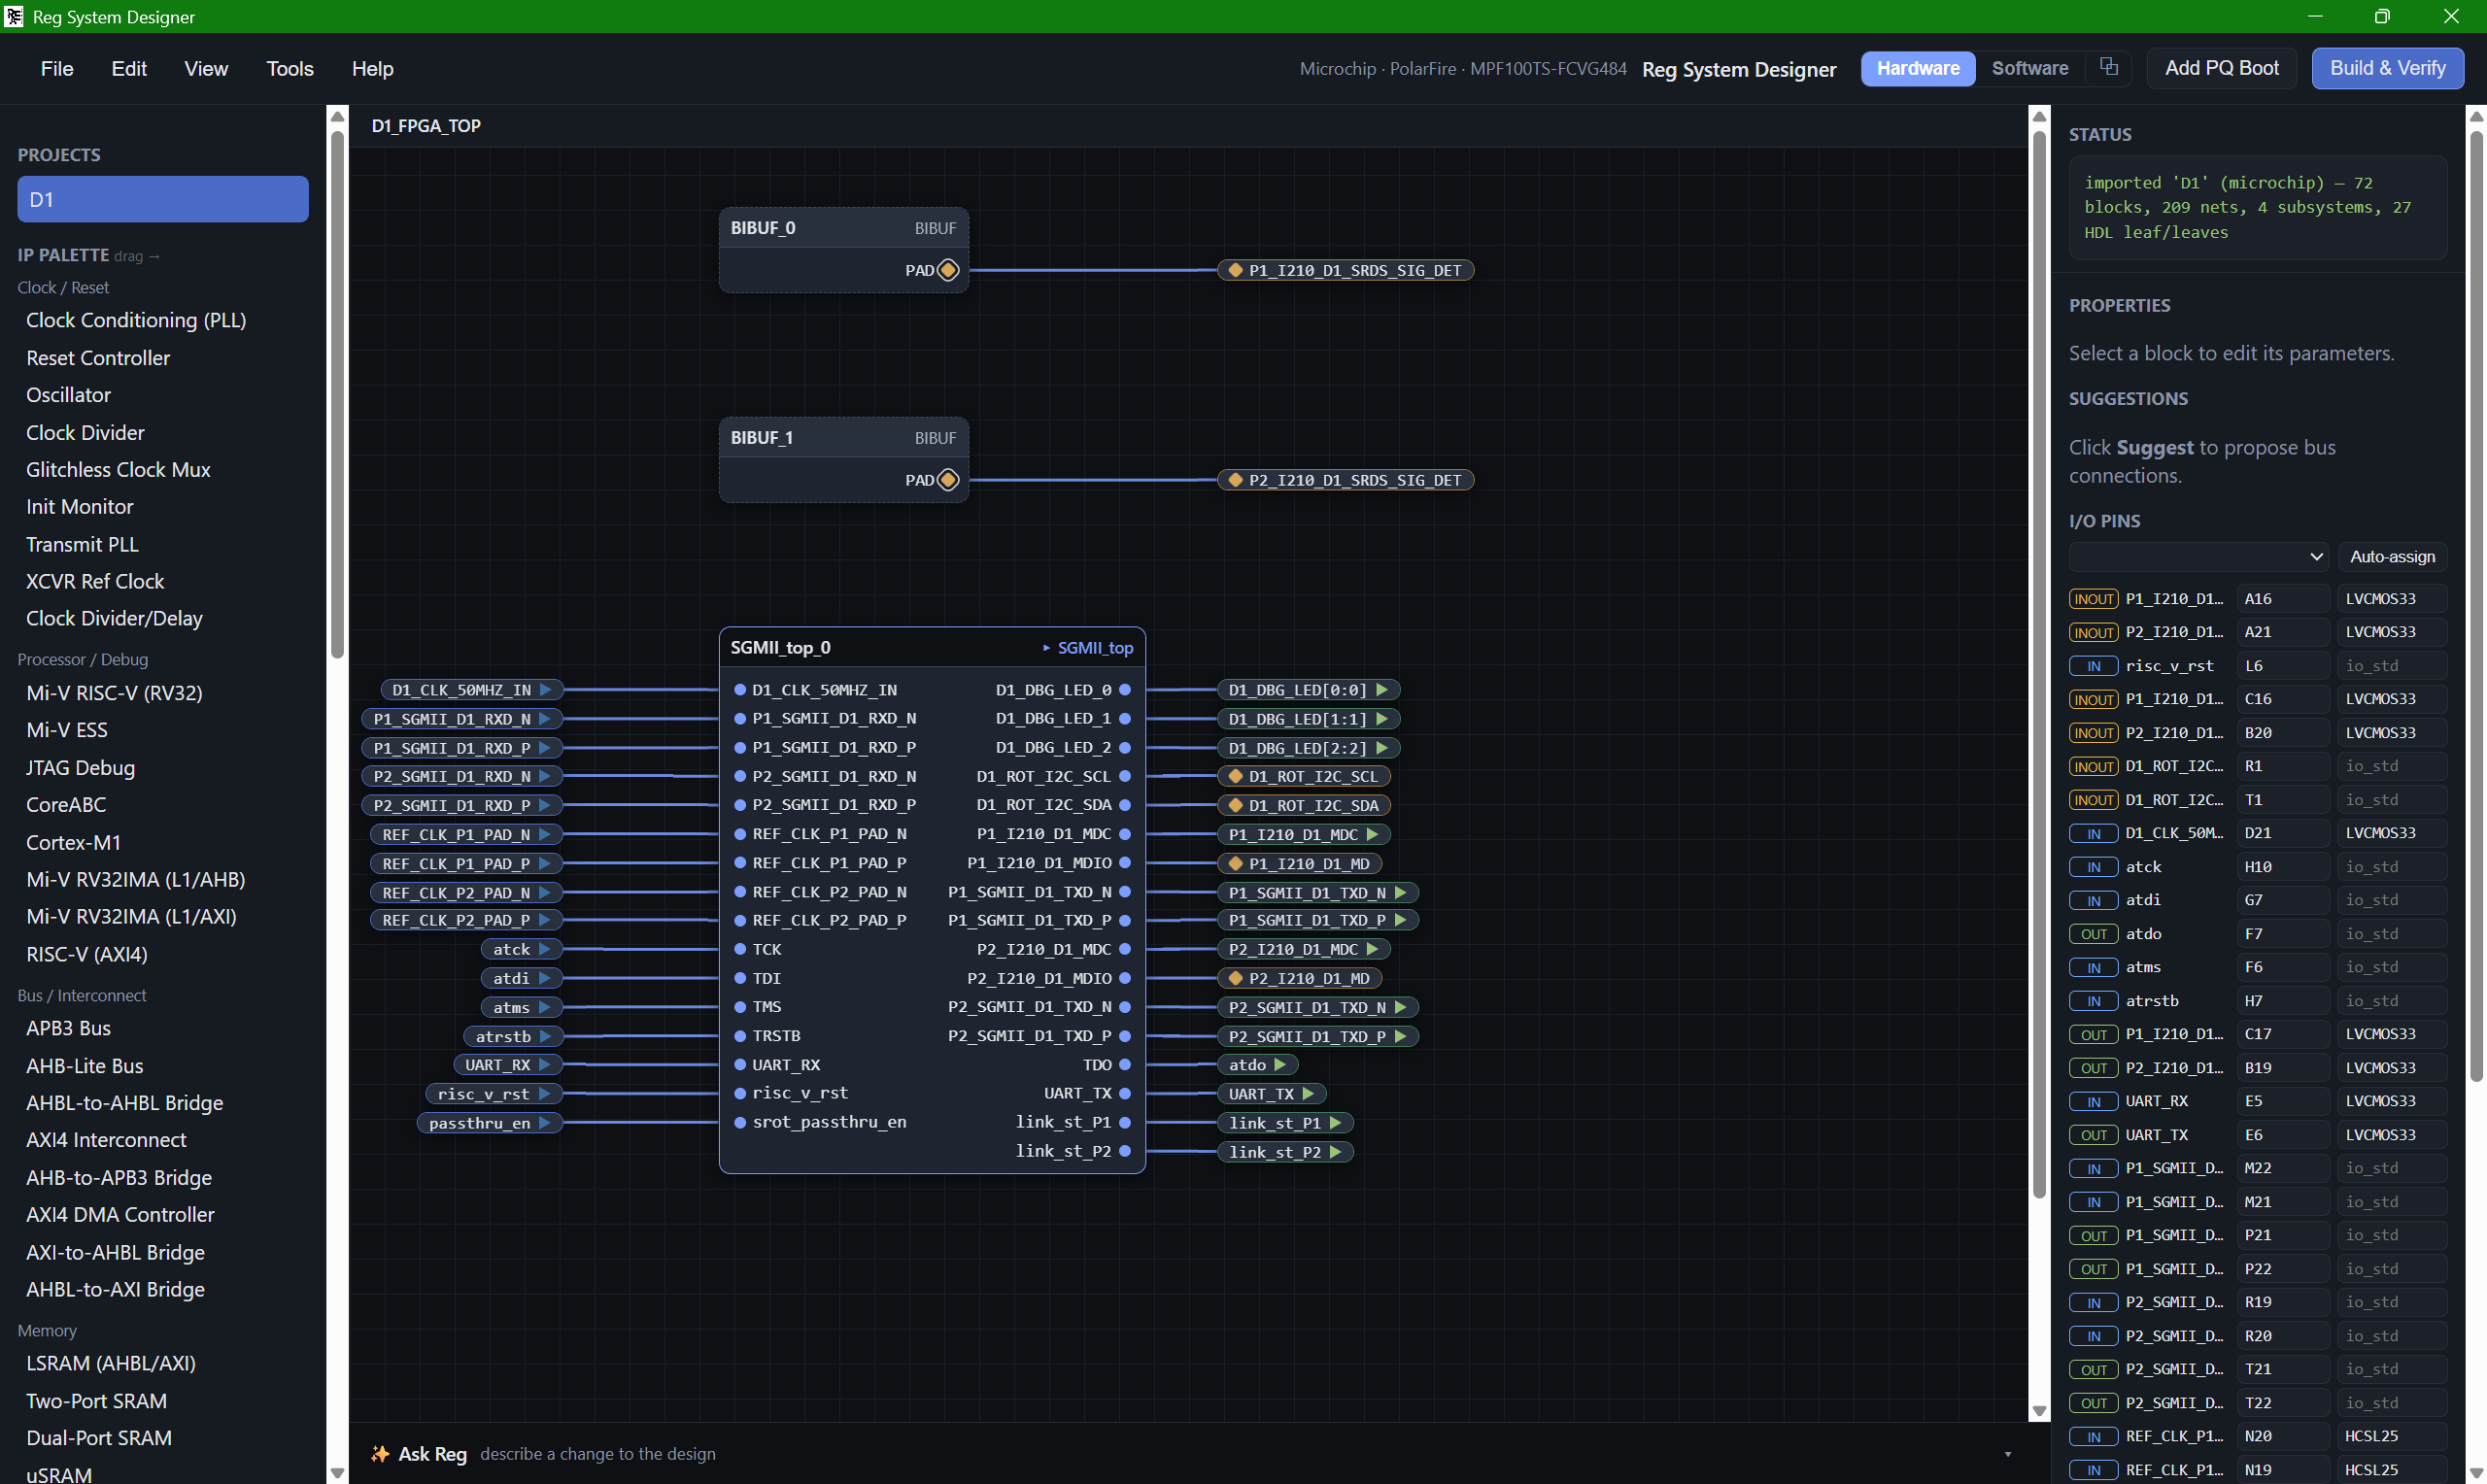
Reg System Designer with a PolarFire design open: top-level block diagram wired to I/O, pin assignments, and Build & Verify controls

Reg's System Designer with a real PolarFire design open — top-level blocks, I/O pin assignment, one-click Build & Verify, and an "Ask Reg" prompt to change the design in plain language. (click to enlarge)
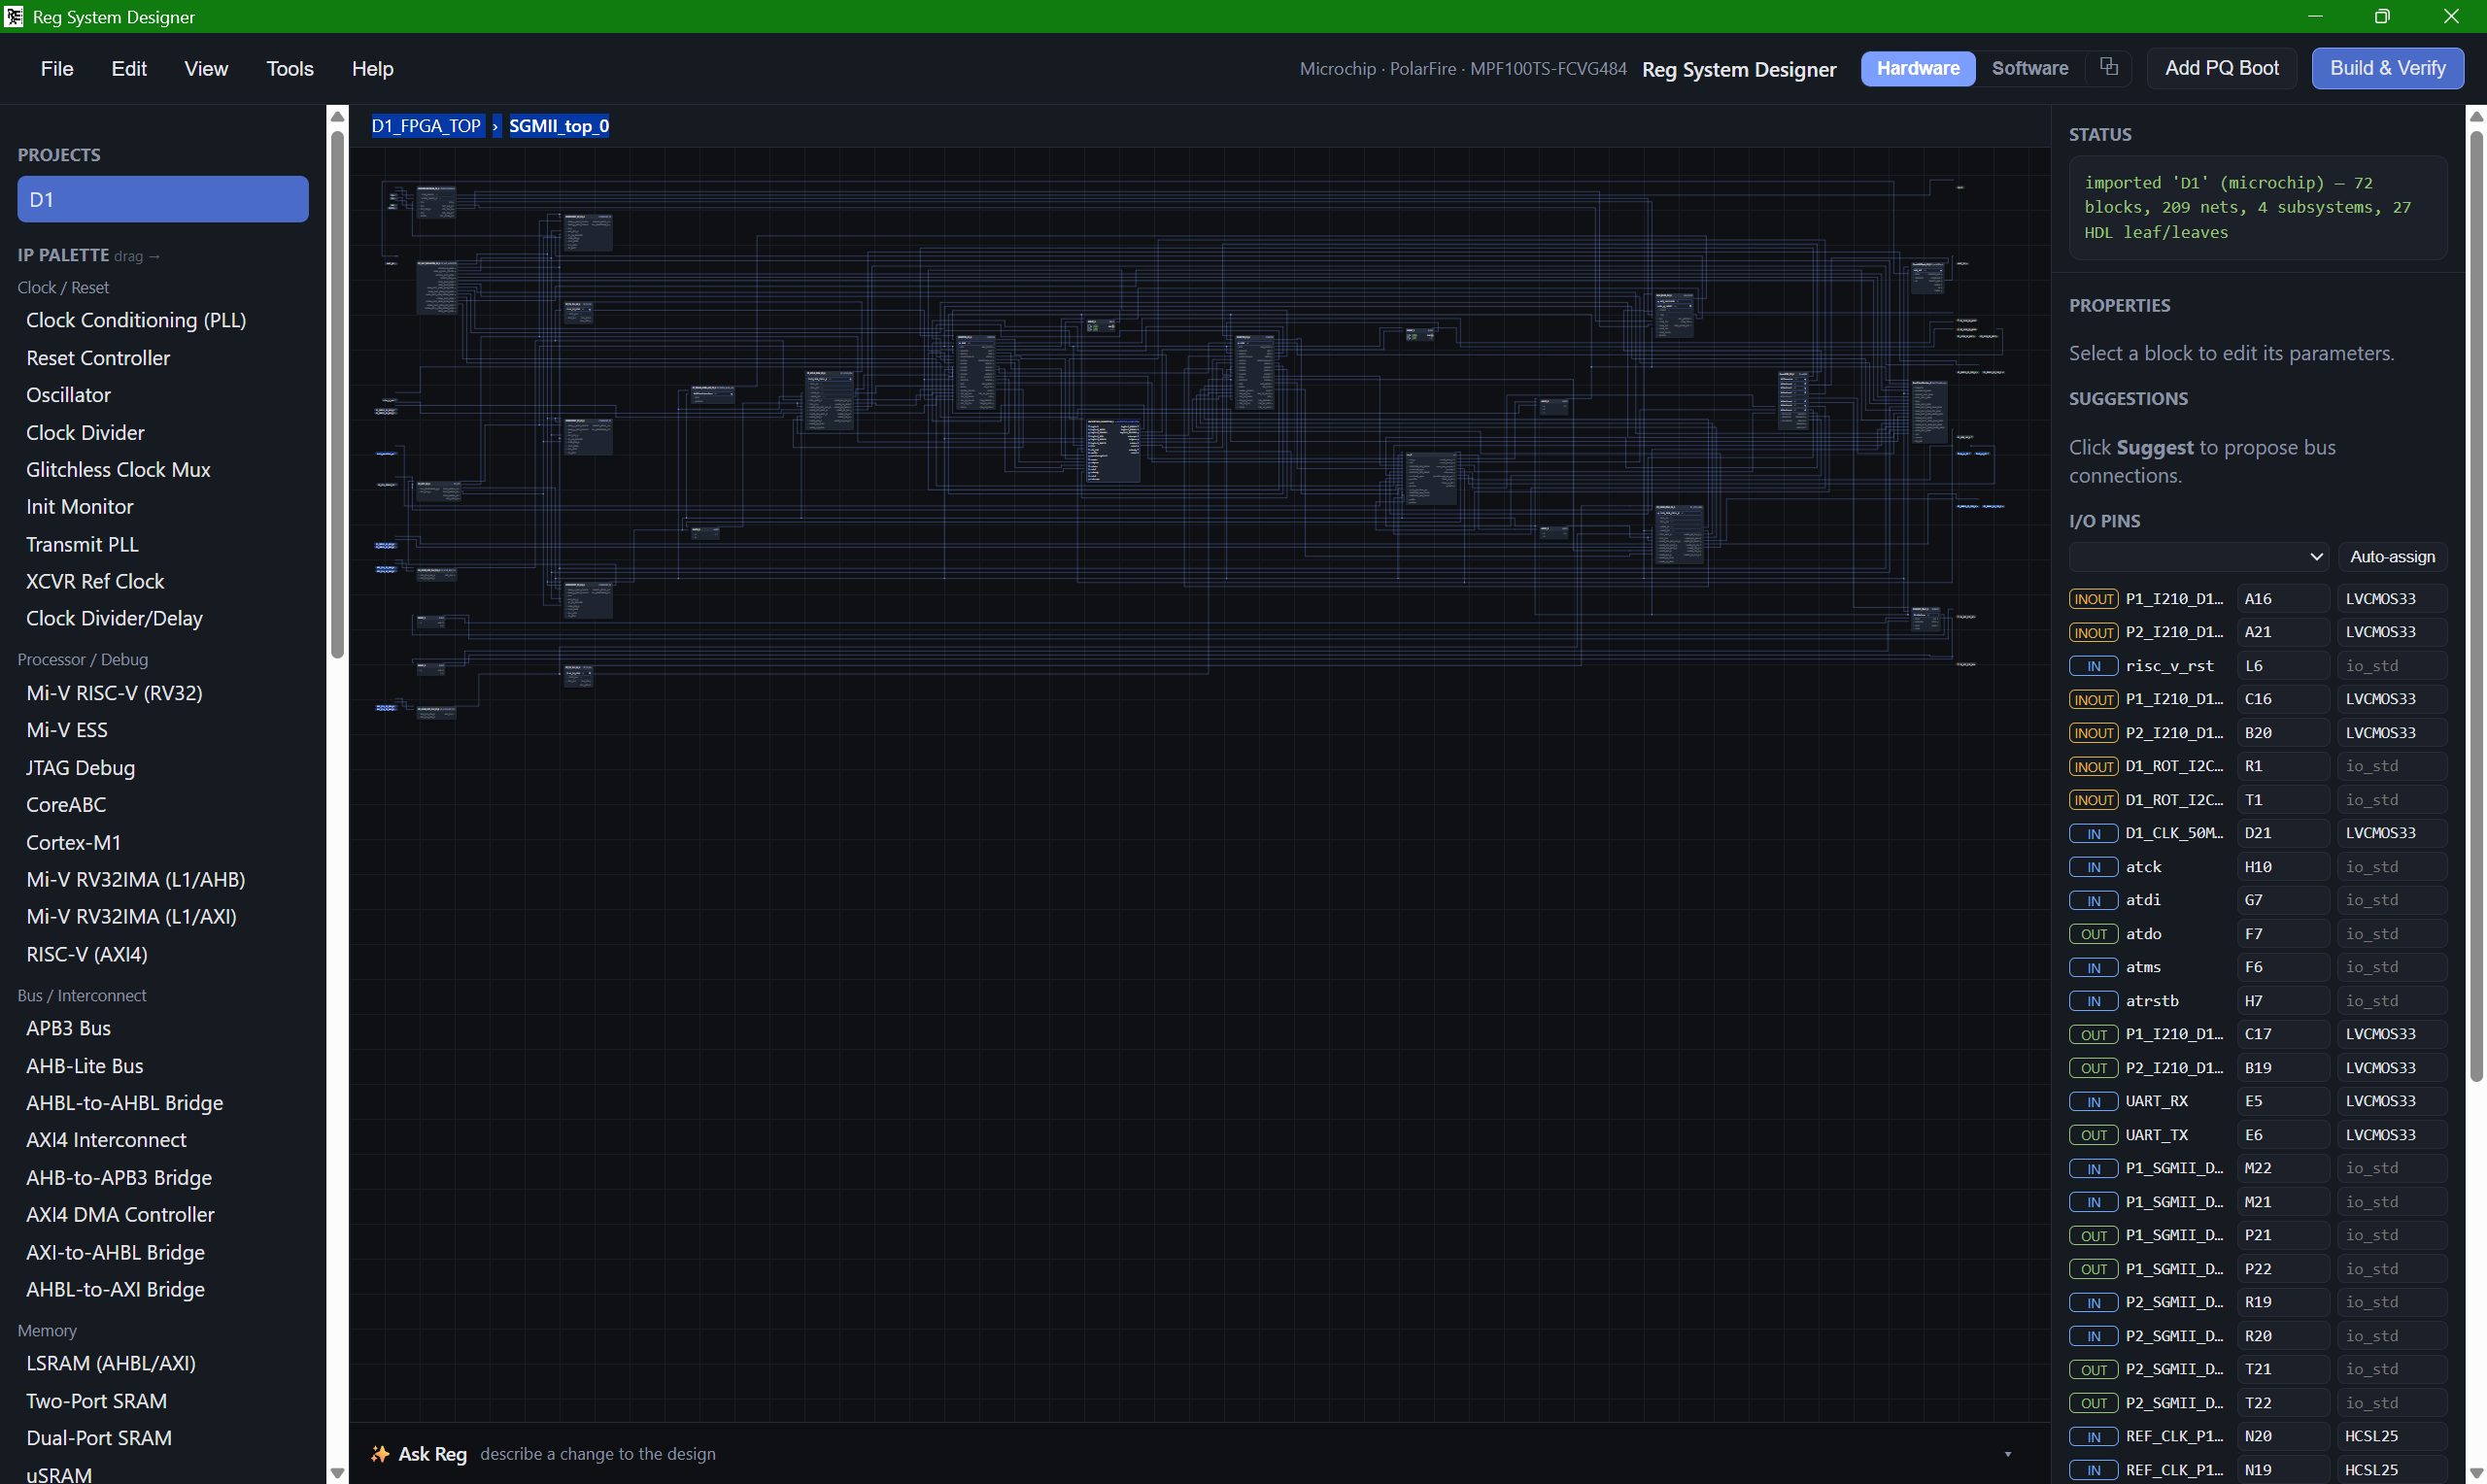
Drilled-in view of the same design in Reg System Designer, showing the full netlist of a subsystem block

Drilling into a single block of the same design: the full wired netlist, one level down. (click to enlarge)
Product literature

The briefs

BootProtect Product Brief
PDF · post-quantum secure boot
Download
Mithril Product Brief
PDF · boot-flash root of trust
Download
Reg Product Brief
PDF · in-boundary AI companion
Download

About RAE

A startup securing the silicon — and the AI — the defense world runs on

Our mission: put the defense world's most critical technology back under its owners' control.

Fielded FPGAs boot through vendor-fused keys and quantum-vulnerable cryptography that can't be patched. Modern AI lives in clouds that CUI and ITAR data can never touch. RAE builds products that close both gaps.

BootProtect (patent-pending Errantry IP, with partner IC-Safety) retrofits post-quantum-resistant, owner-controlled secure boot onto FPGAs already in the field. AES Crypto hardens encryption against power-analysis attacks. Mithril, our HAIR-compliant boot-flash root of trust, keeps host boot firmware encrypted at rest and in transit on platforms that have already shipped. And Reg delivers a frontier-class AI engineering companion entirely inside the customer's security boundary — the same system RAE runs its own engineering on today.

Our founding team brings decades of hardware-security experience from Sandia National Laboratories, Raytheon, and Intel. Alongside the product roadmap, we run a hands-on security-engineering practice: it keeps our products grounded in the hardest real-world problems, and it funds our development.

Founded
2025 · Hutto, Texas
Ownership
U.S.-owned, woman-owned small business
Compliance posture
CMMC Level 2 (self) · ITAR/EAR-aware
Products
BootProtect · AES Crypto · Mithril · Reg
Validation
SiRF PUF assessed by Sandia National Laboratories

Founders & Team

Founded in 2025 by Cylinda Rickert Areno and Matthew Areno

Cylinda Rickert Areno

Cylinda Rickert Areno

Co-founder, Owner & CEO

Cylinda leads RAE's business operations: personnel, finance, contracts, compliance, program management, and communications. As majority owner, she leads RAE as a certified woman-owned small business.

LinkedIn
Matthew Areno, PhD

Matthew Areno, PhD

Co-founder & CTO

Matt sets RAE's technical direction after two decades in hardware security: embedded-systems vulnerability assessment at Sandia, anti-tamper Chief Architect at Raytheon, and Senior Principal Engineer at Intel, where roles included Senior Director of Security Assurance and Cryptography. His PhD research on PUF-enhanced cryptographic units is the line behind BootProtect.

LinkedIn
Trevor Hird

Trevor Hird

Principal Design Engineer

Trevor brings 18 years of FPGA design and security-architecture experience to RAE's product implementations, from RTL through fielded hardware.

LinkedIn

Engineering services

The practice that keeps our products honest

Two decades of hardware-security experience, available on your systems directly — and the reason our products stay grounded in real-world attacks.

01Secure Boot & Anti-Tamper
02Cryptography & Key Management
03FPGA & Silicon Security
04Processor & Platform Security
05Systems Architecture
06Self-Hosted AI Systems
Ask about an engagement →

Customers & partners

Intel
MITRE
Trenton Systems
MMEC — Midwest Microelectronics Consortium
IC-Safety